Anyone who uses coorda entrusts us with something: shopping lists, appointments, birthdays, sometimes things that are nobody else’s business. That is why it was clear to me from the start where this data would live: in Europe – independent, developed in France, under the rules of the GDPR.
One account, no detour
There is one single account for all coorda services, on coorda.me. You sign in there, not via Google, Apple or Meta. Nobody in between learns when you sign in or what you do with us.
No ad profiles, no selling of data
We live from subscriptions, not from your data. We do not sell data and we do not build ad profiles. There is advertising with us all the same – but clearly labelled, chosen by place and never by your entries, without tracking and never as a pop-up.
A cabinet not even we can read
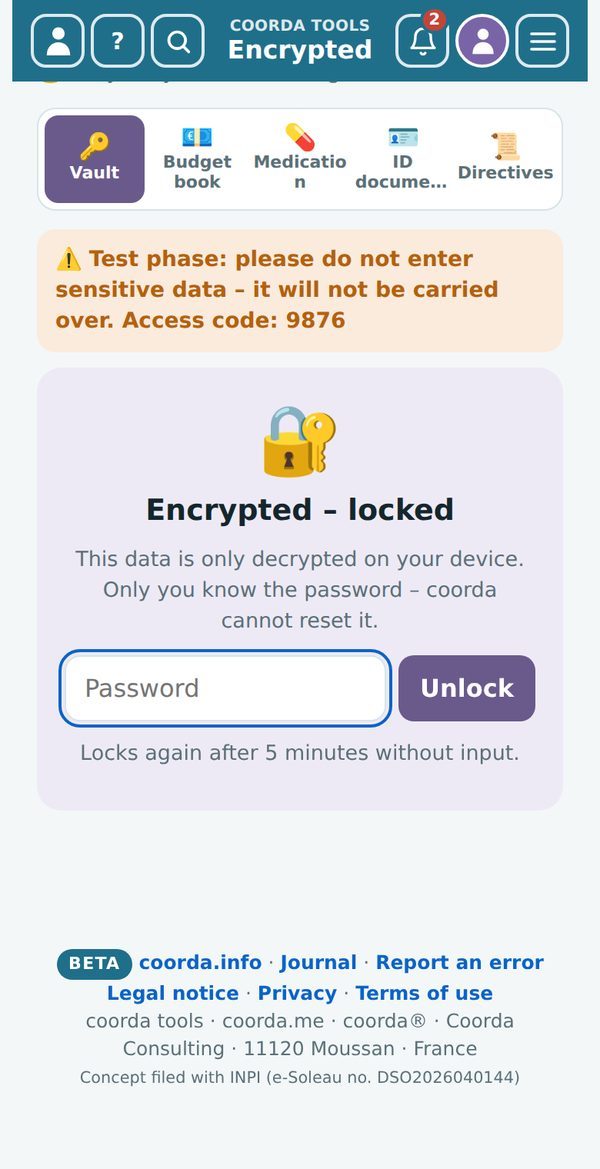
coorda tools has an encrypted cabinet. Whatever you put in it is encrypted on your own device. On our servers there is only a jumble of characters – readable only by whoever knows the password. That also means: if you forget the password, nobody at coorda can recover the data either. After five minutes without input, the cabinet locks itself again.
Important: the cabinet is still in its test phase. It opens with a simple test password that everyone knows and is only there for trying it out and getting to know it. Please do not store any sensitive data there for now – it will not be carried over either.
Why this matters
Data in Europe is subject to European law. You have a right of access, rectification and erasure – and we have to grant it. That is not an advertising promise, it is the framework we work in.
Back in 1997 in the Bresse I learned that the internet lives on trust. Without trust there is no good information and no community. That has not changed.
 aleae: half a century of ideas – and a new guest village for Southern Europe
 2006: Coorda, the synergy people – from La Réunion to the world